Data protection
Data protection training, on a platform that practises it.
Teach your people how to handle personal data, and keep their own learning data under the same discipline. LaserLMS covers both: privacy training with evidence, and privacy controls built into the platform.
Privacy training people actually finish.
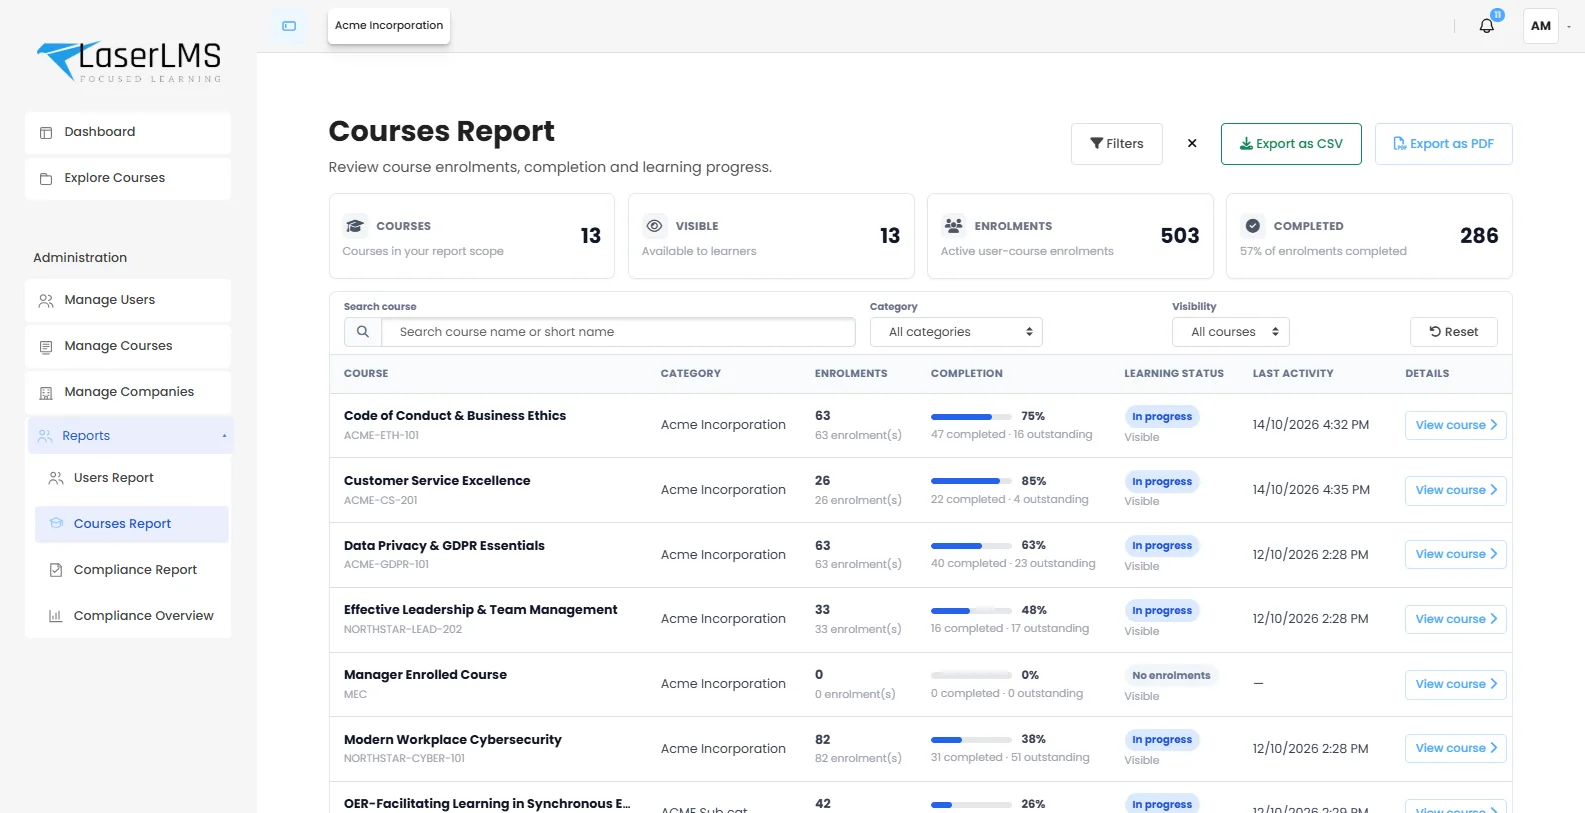
Data protection laws expect staff to be trained and organisations to prove it. LaserLMS handles assignment, reminders, refreshers and evidence, so your data protection officer can answer "who has been trained?" in seconds.
- Core courses for everyone, such as GDPR and India's Digital Personal Data Protection Act essentials.
- Role-specific modules for HR, marketing, customer support and engineering teams who handle personal data daily.
- Policy acknowledgements that record which version of your privacy policy each person accepted, and when.
- Annual refreshers with validity periods so nobody quietly lapses.
- Phishing and security awareness alongside privacy, since most breaches start with a click.
Privacy controls inside LaserLMS
Learning records are personal data too. These controls help you meet your obligations for the people you train.
| Data residency | Dedicated cloud in the region you choose, or on-premises inside your own network. |
|---|---|
| Access control | Role-based permissions, with company managers limited to their own company. |
| Authentication | Single sign-on through your identity provider, and multi-factor authentication for local accounts. |
| Data requests | Built-in workflow to export or delete a person's data on request. |
| Retention | Retention periods by data category, with expired data removed on schedule. |
| Policies and consent | Versioned site policies with an acceptance record for every user. |
| Encryption | HTTPS for all traffic. Encryption at rest configured with your hosting choice. |
| AI processing | Course material is sent only to the AI provider you configure, under your agreement with them. AI features can be switched off. |
| Audit logs | Logs of sign-ins and administrative changes, with retention you control. |
Built with these frameworks in mind
LaserLMS supports your compliance. It does not replace legal advice, and responsibility for meeting each law stays with your organisation.
GDPR and UK GDPR
Lawful processing, data subject rights, retention limits and processor agreements for learners in the EU and UK.
India's DPDP Act, 2023
Notice, purpose limitation, data principal rights and grievance handling for learners in India.
Sector and client rules
Healthcare, financial services and client contracts often add their own training and data handling requirements.
Capabilities behind it
Data protection questions
Something else? Ask us in a demo.
Where is learner data stored?
That depends on how you deploy. A dedicated cloud instance runs in the region you choose, and on-premises deployments keep all data inside your own infrastructure. We confirm hosting locations in writing during procurement.
Will you sign a data processing agreement?
Yes. A data processing agreement covering our role as processor, sub-processors, security measures and breach notification is available for customers.
Can learners request or delete their personal data?
Yes. LaserLMS includes a data request workflow, so administrators can export a person's data or delete it, subject to the retention rules you set for training records.
Do you have training for India's DPDP Act?
You can load your existing DPDP and GDPR courses, or draft new ones from your privacy policy with AI course creation and have your data protection officer review them before release.
Talk to us about data protection.
We will walk through hosting, data flows and privacy controls with your IT and data protection teams.
- Tailored to your use case, not a slide deck
- Cloud, dedicated or on-premises options explained
- Clear next steps and pricing for your scale